DevSecOps
Secure Development
Ship secure software faster and safer
DevSecOps combines DevOps efficiency with advanced security, empowering teams to boost productivity, streamline workflows, and ship secure software faster and safer.
 Key features
What DevSecOps can do
-
01
DevSecOps Integration
Security as a shared responsibility.
Integrate automated security testing at every stage of the software development lifecycle, encouraging seamless collaboration between developers, security specialists, and operations.
SHIFT LEFT SECURITY -
02
Pipeline & Workflow Automation
Streamline & boost productivity.
Empower teams to streamline build workflows, automate CI/CD pipeline triggers, and boost development output without compromising on code security.
CI/CD AUTOMATION -
03
Deployment Management
User-friendly deployment control.
Manage application deployments easily without requiring specialized technical expertise. The platform abstracts complexities so teams can focus on building great software.
EASY ORCHESTRATION -
04
Built-in Security Engine
End-to-end vulnerability scanning.
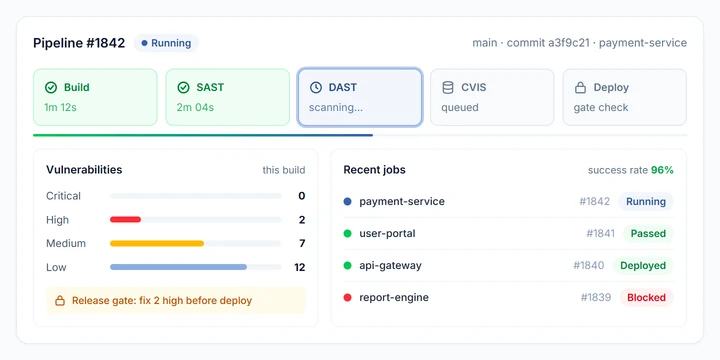
Measure and remediate risks across source code (SAST), active web/API runtime endpoints (DAST), and OS/library container images (CVIS) before reaching production.
SAST + DAST + CVIS -
05
Secure Deployment
Ship quickly and confidently.
Integrate continuous security checks directly into release gates, verifying target SSH credentials, host endpoints, and environment paths prior to execution.
GATEWAY VALIDATION -
06
Real-time Pipeline Monitoring
Full visibility into every rollout.
Comprehensive dashboard providing real-time metrics on successful, failed, and running jobs to ensure smooth rollouts and proactive issue resolution.
TELEMETRY & LOGS
How it works
Secure software delivery in four steps
-
1
Code & Scan (SAST)
Developers push code updates; SAST automatically scans repository sources for early code-level flaw detection.
-
2
Container Scan (CVIS)
Inspect OS packages, application libraries, and container dependencies within the build pipeline.
-
3
Test Runtime (DAST)
Perform automated dynamic security tests against active web services, APIs, and staging endpoints.
-
4
Deploy & Monitor
Ship verified builds to target servers confidently and monitor deployment telemetry on centralized dashboards.
Use cases
Where DevSecOps makes a difference
Built for software engineering teams, SecOps professionals, and enterprises looking to unify security and DevOps.
- Enterprise Engineering & CI/CD PipelinesAutomate vulnerability checks within existing pipelines without slowing down developer velocity.
- Cloud-Native & Containerized WorkloadsScan Docker and container image dependencies (CVIS) before pushing images to production registries.
- Regulated Industries & Compliance AuditMaintain detailed security audit logs, verify SSH credentials, and prove software safety across all releases.
Ready to transform
Let’s build your next intelligent workflow
Talk with BTI about secure AI, data residency, and operational systems built for Indonesian organizations.
Or contact us directly at
contact[@]bti-group.id